透過端對端網路防禦阻斷進階攻擊
Fortinet 安全營運利用整合且自動化的解決方案防禦隱蔽攻擊,以機器速度進行偵測、預防與回應
取得 SecOps ESG 報告 取得聯繫
現今的攻擊者能夠規避傳統的安全防護。Fortinet 安全營運提供進階的網路防禦織網,可在攻擊點阻斷威脅,偵測隱蔽入侵,並自動化您的 SOC,以加速整個基礎架構的協同回應。


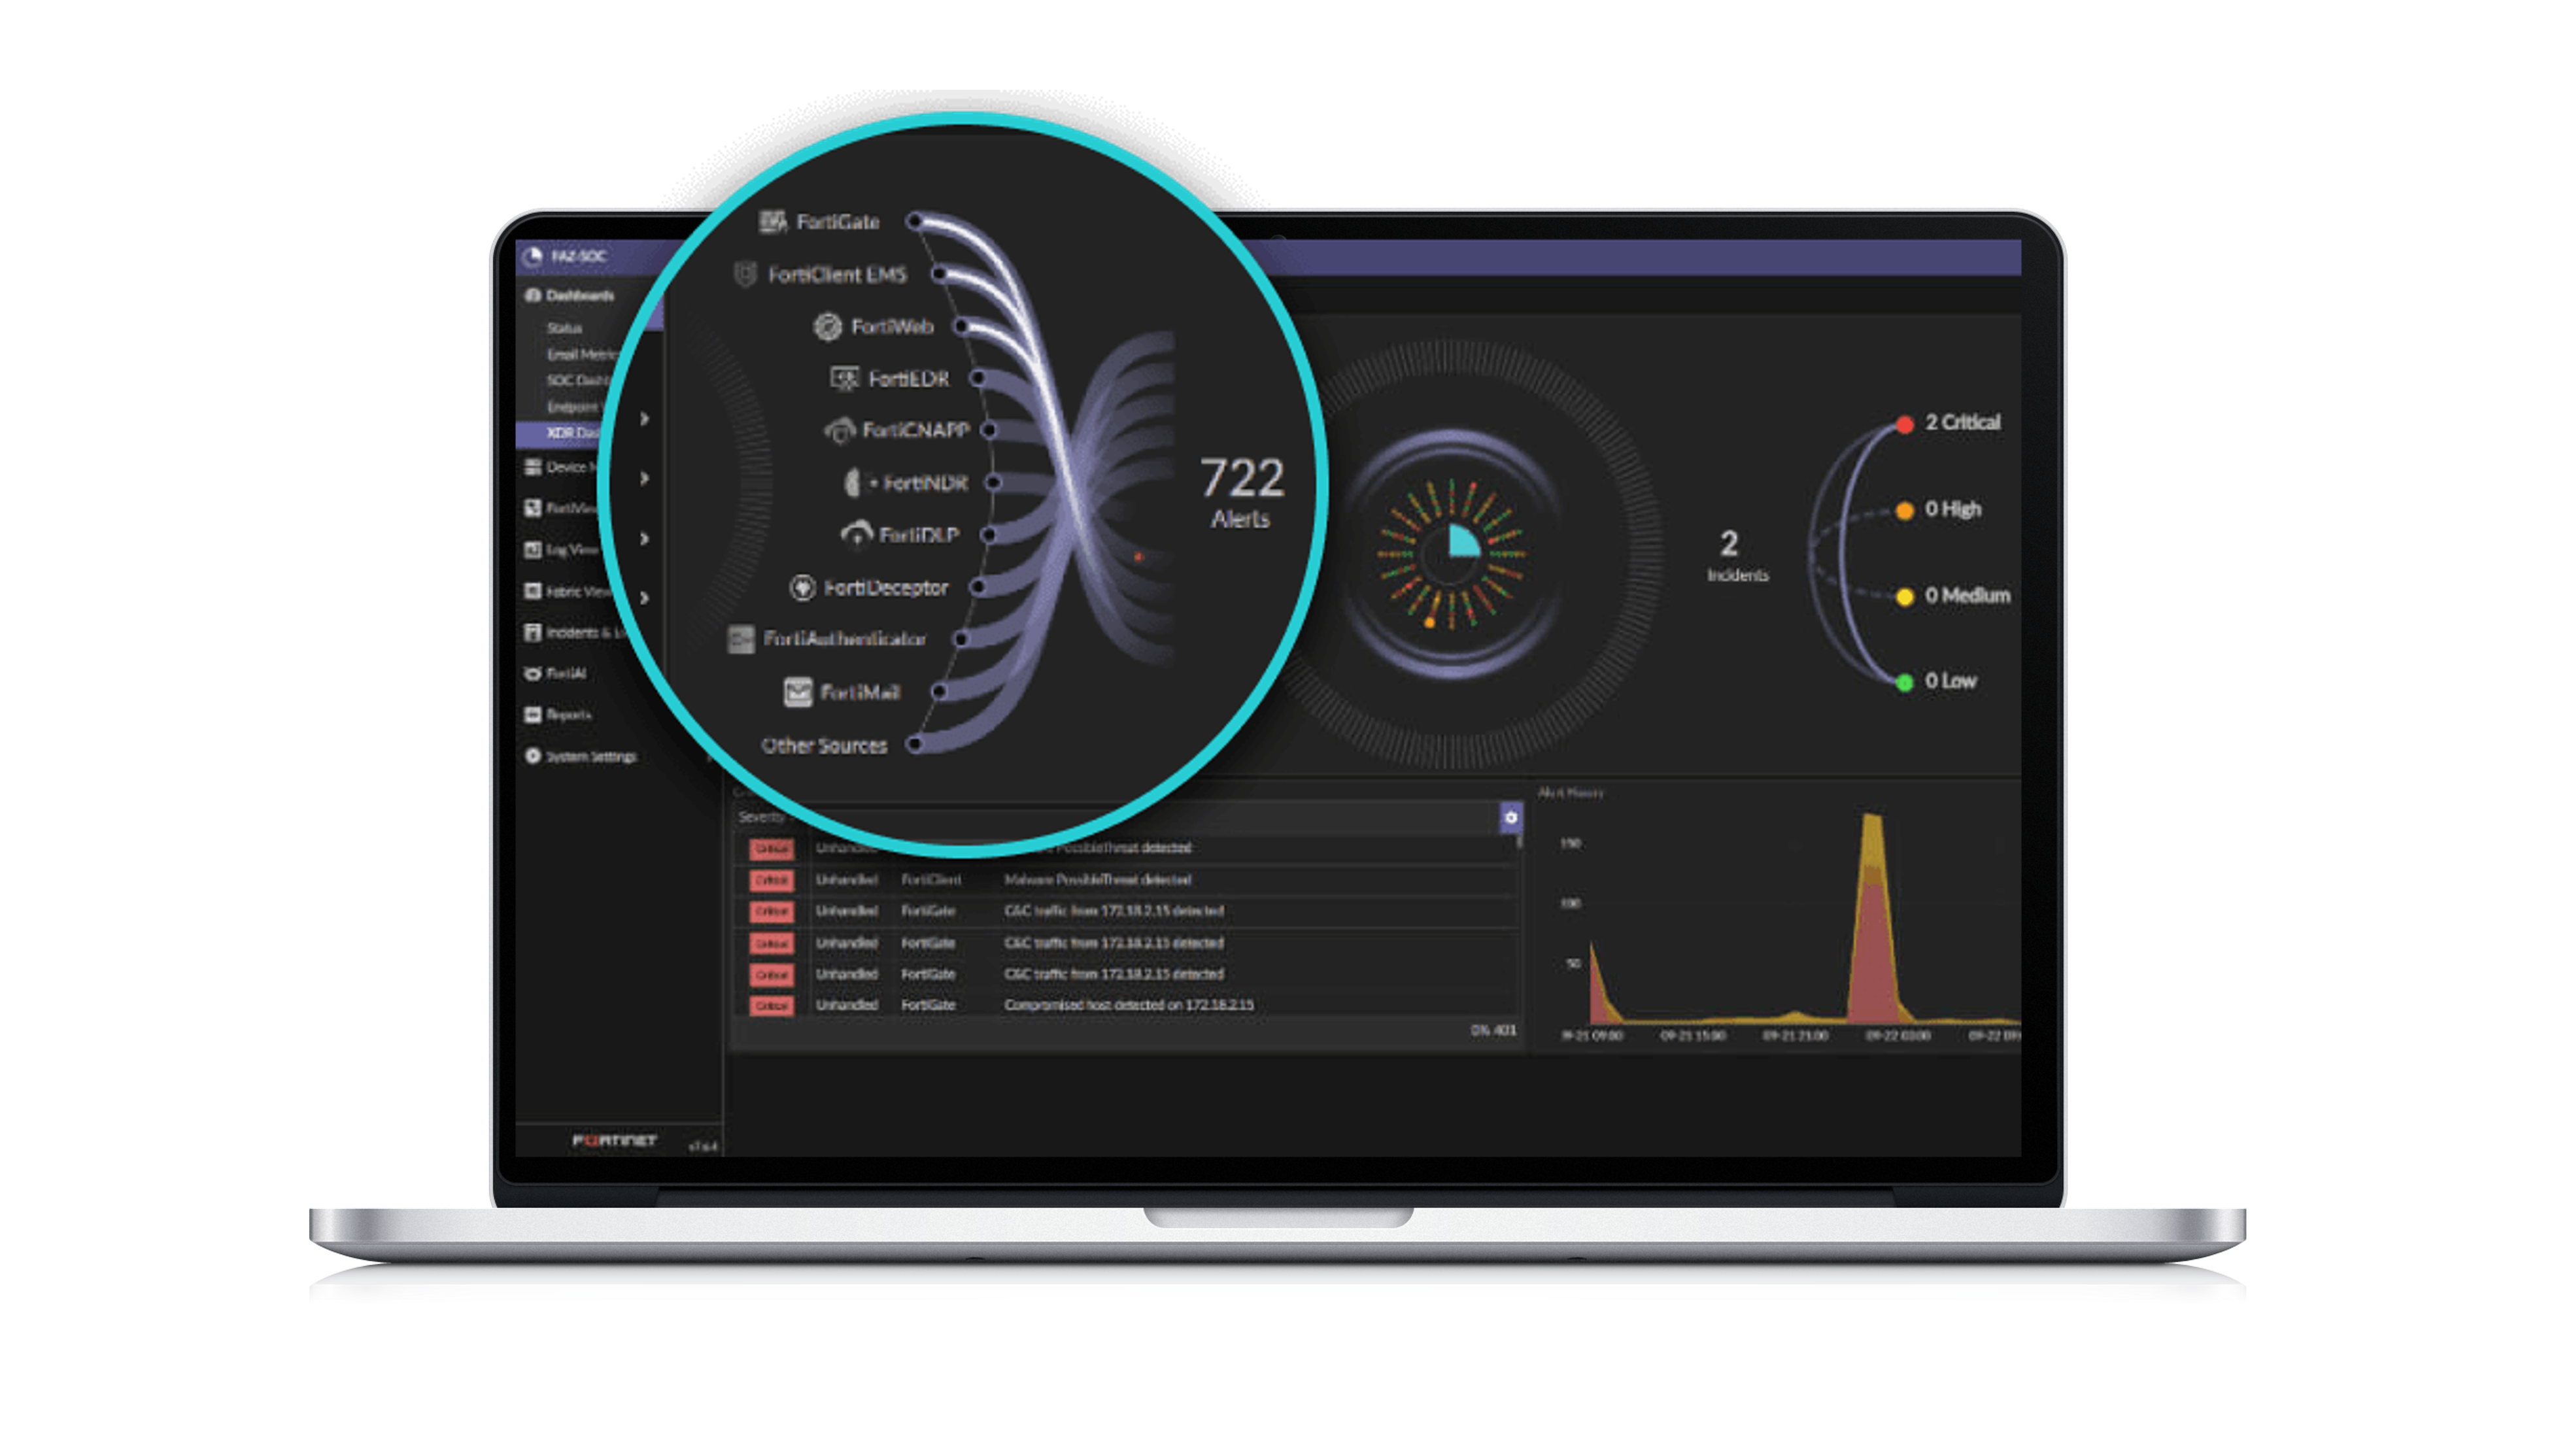
Fortinet SOC 平台整合了來自 Fortinet Security Fabric 和多供應商解決方案的安全事件,提供統一的 SOC 偵測與回應基礎以及託管服務產品,能滿足所有規模之 SOC 團隊的需求。

Fortinet 的統一端點產品可在單一輕量級解決方案中提供端點防護、偵測、安全存取與資料安全。

Fortinet 的網路偵測解決方案結合了無代理程式的網路中繼資料分析與誘捕技術,確保整個攻擊面的完整可視性,並偵測橫向移動、C&C 及資料外洩等進階攻擊者活動。

我們的資料與郵件安全解決方案可保護使用者生產力與敏感資料,抵禦可能導致資料外洩的外部威脅與內部風險。這包括對電子郵件、協同作業與檔案共用、SaaS 應用程式、GenAI 使用與網頁瀏覽的保護。
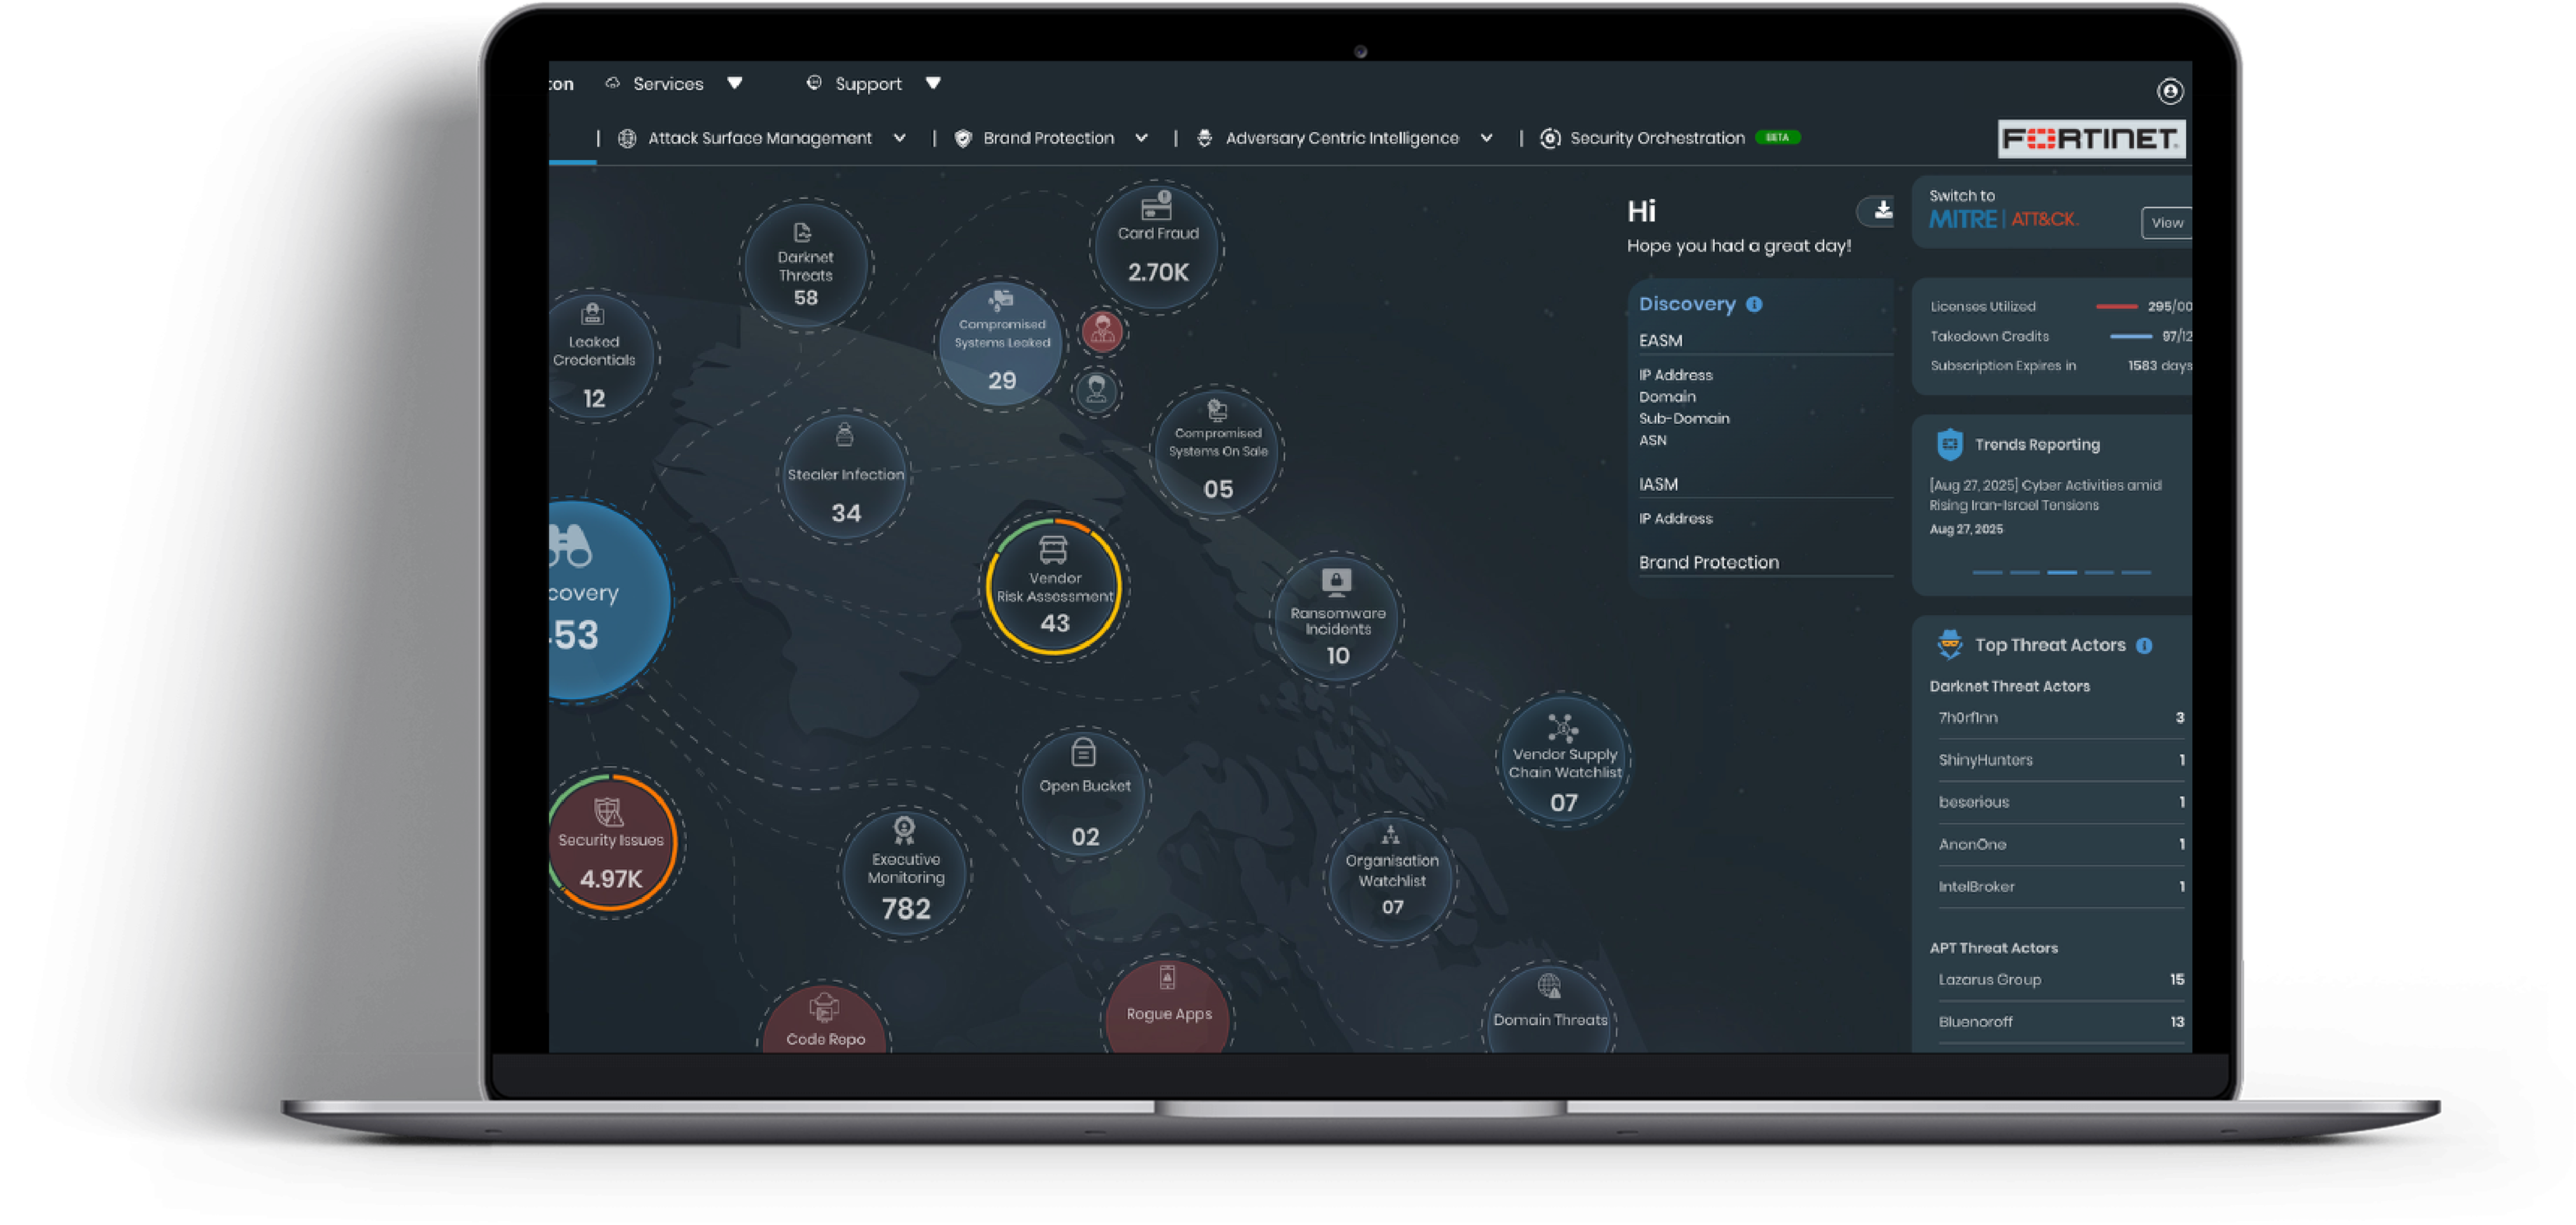
我們的解決方案結合了攻擊面管理、對抗性曝險驗證以及數位風險與品牌保護,可發掘、排定優先順序並修復對您的企業構成最大風險的曝險問題。

Fortinet IAM 解決方案將身分轉變為您新的安全邊界。這些解決方案透過集中式指揮中心取代零散的登入防護,該中心會在每個實體存取您的資料前進行驗證。

Fortinet 安全服務可提供 24x7 全天候 SOC 監控以及專家威脅調查與回應指引、專注於端點的監控、資安事件回應服務,以及其他為滿足您的安全增強需求而自訂的服務。

Fortinet 的 SecOps 產品組合是一套解決方案與服務,有助於在所有攻擊點為您提供防禦,確保有效的 SOC 運作,並提供專家服務以最低成本強化您的組織。
 FortiSOC
 FortiAnalyzer
 FortiSIEM
 FortiSOAR
 FortiGuard 安全營運中心即服務
 FortiEDR
透過輕量級代理程式,自動且高效率地即時識別並阻止入侵

透過輕量級代理程式,自動且高效率地即時識別並阻止入侵
 FortiAuthenticator
 FortiToken
 FortiPAM


此報告提供 SOAR 市場的深入概觀、重大趨勢,以及詳細的供應商比較,以協助讀者選擇最適合其需求的解決方案。
FortiSOAR 支援生成式 AI、OT 環境、法規遵循與 IT/NOC 營運等進階功能,以及企業、政府與服務供應商組織的高採用率,提高了其領導地位。


FortiAnalyzer Ordering Guide

FortiSIEM Ordering Guide

FortiDeceptor Ordering Guide

FortiSOAR Ordering Guide

FortiSandbox and FortiGuard Sandbox Service Ordering Guide

FortiRecon Ordering Guide

FortiNDR Ordering Guide

FortiSIEM Datasheet

FortiSOC delivers a unified SaaS offering that brings together SIEM, SOAR, identity threat detection, threat intelligence, and more into a single platform experience powered by agentic AI.

Delivering out-of-the-box value, complete flexibility, and ultimate scale, FortiSIEM is the right solution for organizations and managed security service providers (MSSPs) of any size.
With the Fortinet SOC platform, security teams of any size can swiftly identify and respond to threats using advanced detection, automation, and generative AI (GenAI) assistance.
For proactive and resilient security, the SecOps journey should begin with foundational solutions that can be enhanced and scaled over time to build a centralized, AI-driven security operations center (SOC) with adaptable incident response.

Generative AI (GenAI) offers a transformative opportunity for SecOps teams to enhance decision-making, streamline operations, and improve the organization’s overall security posture.